

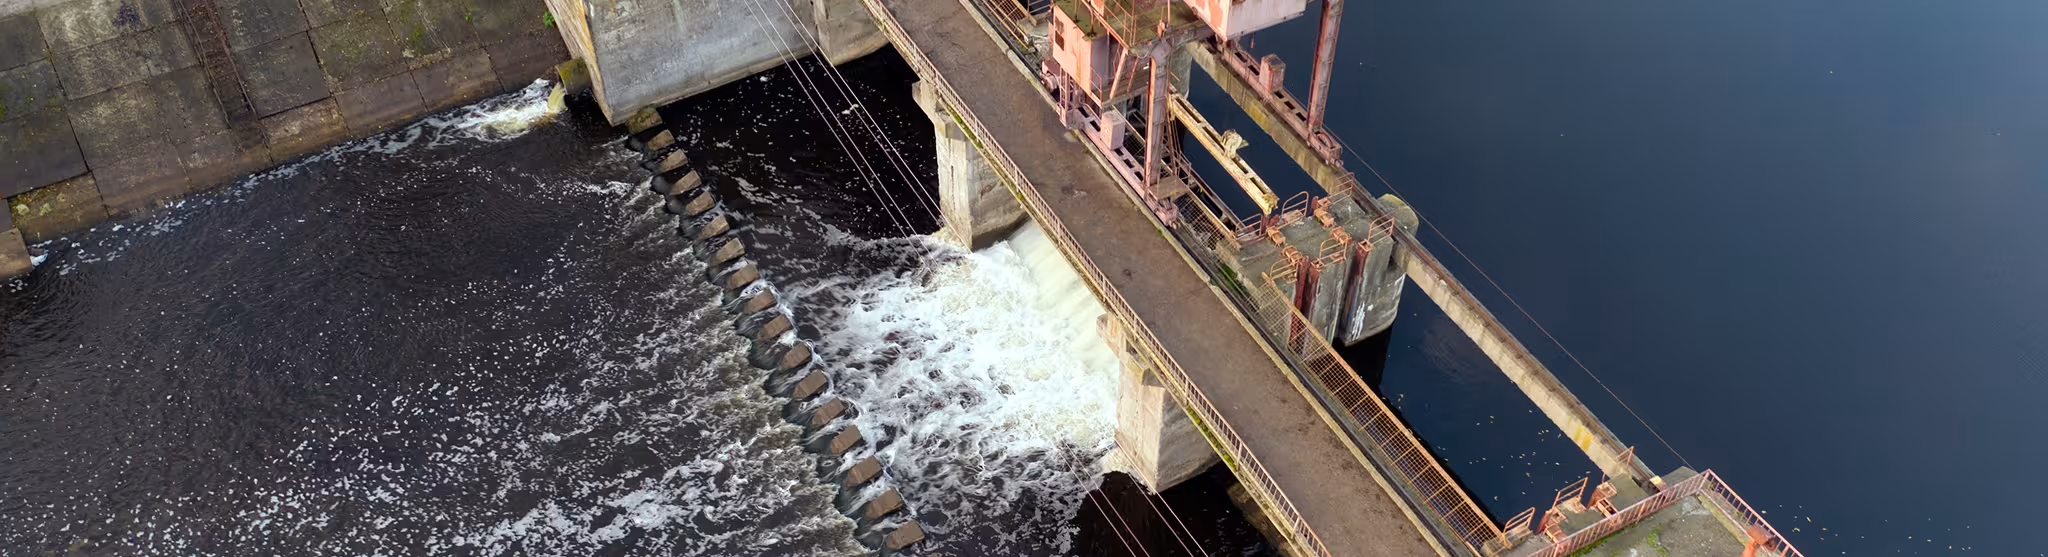
Water and wastewater management
24/7 IT/OT security monitoring and incident management: infrastructure continuity and public health protection
Control systems in water and wastewater management maintain water supplies and sanitary safety — disruption can directly affect public health.
We provide continuous monitoring, event analysis and incident response according to agreed procedures across IT and OT environments — from SCADA systems to production infrastructure.
We analyse events from IT infrastructure and the agreed SCADA and OT systems within the service scope to identify anomalies, threats and availability issues. Data sources and response methods are tailored to the environment and service criticality.
Enterprise combines 24/7 NOC and SOC operations with visibility of covered assets. Permissions, priorities and times for taking up cases are defined in the service specification.
Our services support compliance with NIS2 and critical infrastructure requirements.
How do we support continuity of critical water and wastewater infrastructure?

24/7 IT security monitoring
We monitor IT and OT systems, SCADA and water and wastewater infrastructure in real time.

Event correlation (SIEM/XDR)
Correlation and automated analysis of data from agreed sources help identify threats. The SOC team assesses alert context and acts in line with its permissions and the escalation procedure.

Incident management
Every event is analysed and handled in accordance with critical infrastructure procedures.

Rapid response and escalation
We respond around the clock, minimising the impact of incidents on operational continuity and sanitary safety. Detection time determines incident impact.
Failure to detect incidents threatens public health protection
In water and wastewater management, a security incident can affect the continuity of water supplies and residents’ sanitary safety.
SCADA systems, production infrastructure and IT are interconnected.
A single event — ransomware, interference with a control system or an operational error — can disrupt the entire infrastructure.
The problem is not a lack of tools.
It is a lack of real-time response.
Alerts remain unanalysed while incidents develop before they are detected.
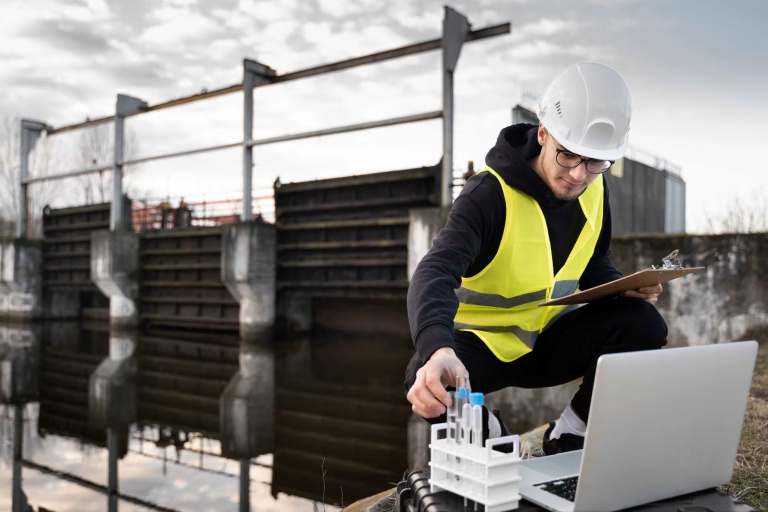
Ransomware protection for water utilities — SOC and Enterprise scope
For water and wastewater utilities, a successful ransomware attack is a major threat: encryption of engineering workstations, SCADA servers or billing systems threatens the continuity of water treatment and wastewater processing. Relying solely on restoring the IT/OT environment from backups means lengthy outages, disrupted water supplies for residents and the risk of substantial financial penalties under the NIS2 Directive and Poland’s National Cybersecurity System Act (KSC).
In SOC and Enterprise, analysts review agreed data from IT infrastructure and agreed SCADA and OT systems around the clock. They verify alerts, determine incident scope and perform authorised containment actions, such as endpoint isolation or session revocation, where tools and permissions allow. Enterprise combines this with NOC. Acknowledgement times, escalation and communication rules are defined in the service specification. OT actions must account for process safety and be agreed with the operations and maintenance team.
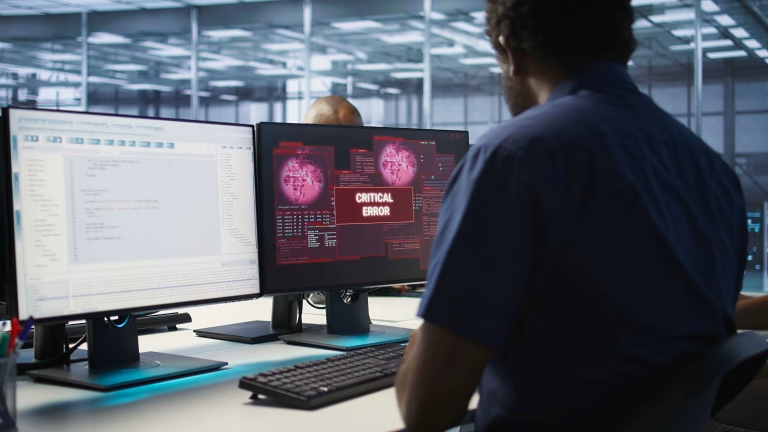
Can your organisation detect an incident in time? Find out before an attacker does
In many companies, the problem is not a lack of tools — it is a lack of response. You may not know who analyses alerts at night, how quickly incidents are detected or whether your organisation meets NIS2 requirements. That leaves you without effective control over security. We assess your environment, identify gaps in detection and response, and propose a SOC model aligned with your actual risks.

Water and wastewater management
Managing incident risk in the water sector — why are backups alone not enough?
When systems controlling water treatment, distribution or wastewater processing fail, the impact immediately extends beyond IT, threatening customers and the environment. Unavailable SCADA systems mean loss of control over industrial processes, billing failures interrupt settlements, and damaged telemetry databases prevent water quality reporting to supervisory authorities such as GIOŚ and Sanepid.
Most incidents in the water sector begin in IT — through phishing targeting office staff, an infected USB drive on an engineering workstation or a vulnerability in remote maintenance access to OT devices. Once inside the network, an intruder quietly explores the infrastructure. Backups protect data from permanent loss but do not prevent attackers from taking control of controllers or stealing data.
Enterprise combines SOC security operations with NOC availability operations. The teams jointly set priorities, perform approved actions and document the incident. This model supports operational resilience; the full organisational, technical and legal requirements are defined separately through GRC.

24/7 IT security monitoring
We monitor the agreed scope of IT systems and agreed data sources from OT installations. Visibility depends on connected sources and telemetry quality; we identify and address gaps in data delivery within the service scope.

Event and alert analysis
Every alert is analysed by the SOC team. We eliminate false positives and identify real threats. Alerts alone do not constitute security monitoring.

Data correlation (SIEM/XDR)
SIEM combines and analyses data from multiple systems to help identify related events. Integrations can trigger approved automated actions. SOC provides rule oversight, context assessment and incident handling within the agreed scope.
Recovery readiness
NOC oversees agreed backup jobs, while Enterprise includes representative restore tests. Backup locations, retention, immutability and multi-region architecture are defined separately within backup and disaster recovery services.

Anomaly detection
We identify unusual user and system behaviour — often before it develops into an incident.

24/7 incident response
Following alert analysis, we initiate approved actions to contain the threat. Response priorities and methods account for the impact on services, available permissions and the client’s procedures.

Incident management
We manage incidents from detection to closure, with full documentation and accountability for actions taken.
Questions and answers
Answers to frequently asked questions:
Which package meets NIS2 requirements for the water and wastewater sector?
Monitoring, NOC, SOC and Enterprise differ in visibility and responsibility for handling outages and threats. The services support monitoring, response, operational resilience and documentation. No plan on its own establishes full organisational compliance; audits, the ISMS, documentation and expert roles are defined within the GRC scope.
How quickly will you restore our systems?
Service restoration time depends on the agreed RTO, available backups, recovery infrastructure and system dependencies. NOC oversees backup jobs, while Enterprise includes agreed representative restore tests. Backup storage, replacement resources and BaaS/DRaaS services require a separately defined scope. A response SLA does not guarantee restoration time.
Does protection cover SCADA systems and OT infrastructure?
Scope may include agreed servers, databases, engineering workstations and SCADA/OT telemetry sources. Monitoring and response actions are agreed with process owners and automation teams, taking plant safety into account. Configuration backups, machine images, recovery infrastructure and RTO/RPO objectives require separate agreement and testing.
What happens if ransomware encrypts our environment?
We coordinate recovery according to the agreed plan and service scope. Backups, retention, immutability and BaaS/DRaaS infrastructure are covered by a separate agreement. Enterprise includes oversight of recovery readiness and agreed representative tests, without automatically providing backup storage.
How do you prepare documentation for NIS2 inspections and audits?
We provide operational reports and records of actions covered by the selected plan. Results of agreed recovery tests supplement these materials. Gap analysis, mapping controls to requirements and support during an organisational audit are delivered as a separate GRC scope.
Contact
Could not find an answer to your question?
We will be happy to answer your questions. Choose the contact method that works best for you.
or

