
About us
Security begins with incident detection and a timely response
VigilHorizon brings together SOC and NOC specialists. Within the agreed scope, we analyse threats, carry out authorised incident containment and support service availability around the clock.
We bring together experience in infrastructure operations, fault handling and cybersecurity. Our services address concrete organisational needs: visibility into system health, threat analysis and agreed response. Monitoring scope, team responsibilities and working arrangements are defined before the service starts.
Meeting standards is not enough. Security needs to work in practice.
Meeting formal requirements does not mean being secure.
An organisation can have EDR, SIEM and procedures, yet still fail to detect an incident in time.
An alert is a signal that needs assessment in the organisation’s context. SIEM can analyse events automatically and trigger configured actions, while the team is responsible for rules, escalation and response oversight. We define this division of responsibilities as part of the service.
VigilHorizon provides operational capability:
• 24/7 IT security monitoring and analysis
• event correlation (SIEM / XDR)
• incident management
• response playbooks
• accountability for actions
We combine technology, processes and people into one operational security system.
Our mission
We connect threat detection with authorised response
We build operational IT security around 24/7 incident detection, analysis and response. We go beyond tools and monitoring to provide the ability to act when an incident occurs. Our solutions deliver continuous 24/7 event analysis, data correlation and a prompt threat response, supporting organisations in maintaining IT stability and security.
We connect threat detection with operational response to contain incidents and limit their effect on the organisation. The service includes 24/7 incident analysis and handling within the agreed environment, with defined procedures and permissions.
Why VigilHorizon?
• experience with real security incidents
• an operational 24/7 SOC, beyond monitoring alone
• SOC, NOC and observability integration
• accountability for incident response
We do not supply tools.
We provide the ability to act when an incident occurs.
Our values
Trust, collaboration, accountability
People
They are the source of our strength. We maintain a business environment that encourages motivation, teamwork and commitment through honesty, trust and mutual respect.
Respect
Respect guides all our daily interactions: with each other, with our clients and even with our products.
Integrity
We strive to uphold the highest standards of ethical conduct in fulfilling our responsibilities to clients, suppliers and the community.
Founders
VigilHorizon was founded by Jakub Marciniak and Hubert Pasternak.
The founders combine experience in infrastructure operations and cybersecurity. We tailor VigilHorizon services to the team’s needs, from monitoring and automatic alerts to round-the-clock handling of faults and security incidents. NOC, SOC and Enterprise plans also define responsibility for actions, permissions and escalation rules.
It is the operational ability to:
• detect an incident
• analyse a threat
• respond to incidents in real time
24 hours a day.
We build solutions that combine threat detection, analysis and agreed response to limit the business impact of incidents.
Co-founders
The people behind VigilHorizon
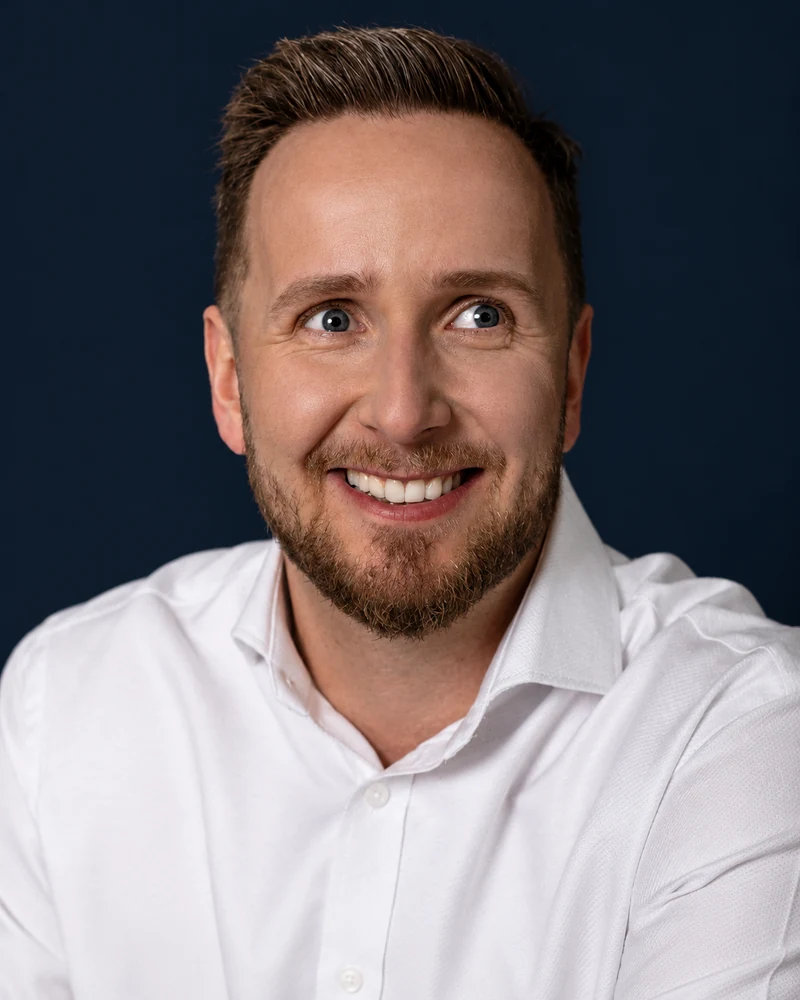
Jakub Marciniak
CEO
Co-founder and CEO of VigilHorizon. He leads business development, sales and marketing, as well as relationships with clients and partners. His focus is on building the brand, developing the service offering and clearly communicating the value of cybersecurity services. He combines knowledge of the IT sector with an understanding of clients’ business goals, helping them define their needs and the scope of cooperation. He works with the technical team to align proposals with each organisation’s priorities, capabilities and scale. His approach centres on a clear sales process, lasting partnerships and the company’s long-term growth.
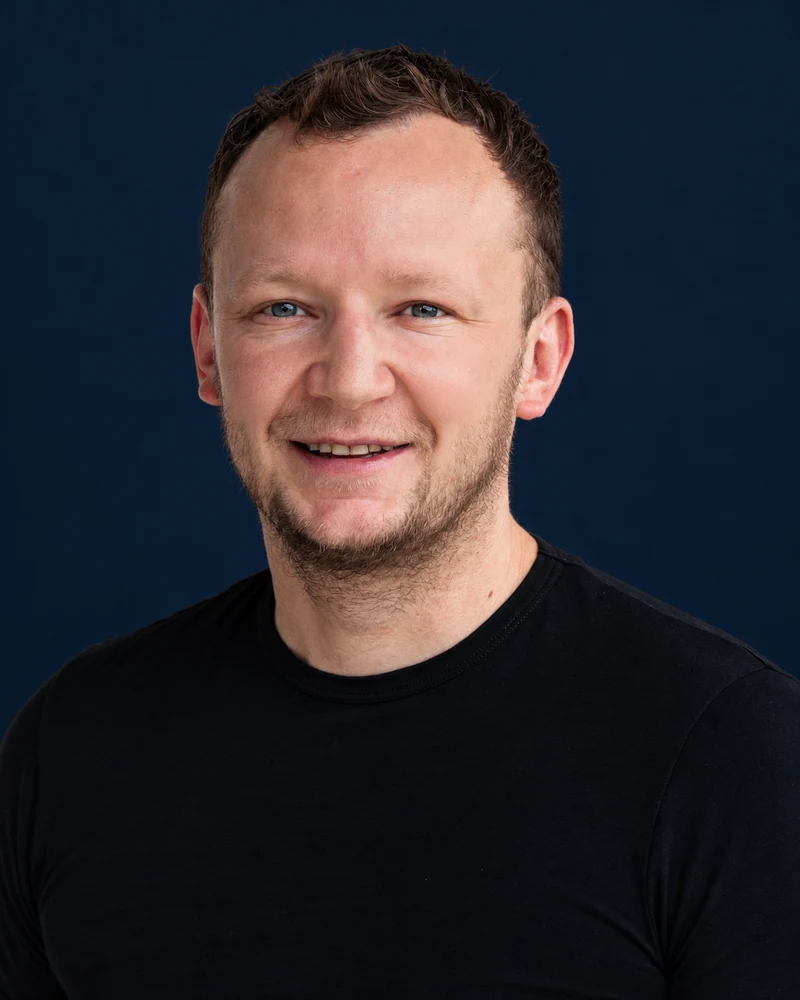
Hubert Pasternak
CISO / CTO
Co-founder and CISO / CTO of VigilHorizon. He is responsible for the company’s technology direction and the security strategy behind its services. He connects IT architecture development with risk management so that technology decisions support business goals and organisational resilience. He oversees the selection and integration of solutions, security standards, and incident detection and response processes. He supports technical teams in translating requirements into coherent, scalable solutions. His approach centres on informed technology decisions, clear responsibilities and continuous improvement of the protection provided to client environments.
Educational scenarios
From a signal to decisions and action
Explore how SOC and NOC teams can work together in different situations. Each scenario presents an assessment, possible actions and their limitations.
1 / 6
Suspicious logins in a production environment
Situation and assessment
Unusual logins outside office hours may indicate account misuse or require another explanation. SOC analyses events from the agreed sources and establishes their context.
Team actions
Once a threat is confirmed, possible actions include restricting access, isolating a specified asset and coordinating with production operations, within the granted permissions.
Aim and limitations
The aim is to limit incident spread. Decisions must account for production process safety; they do not guarantee uninterrupted operation.
Unusual traffic and reduced shop availability
Situation and assessment
Increased shop load and unusual traffic may result from demand, a fault or an attack. NOC checks availability and performance while SOC examines signs of abuse.
Team actions
Correlating data helps establish the cause. Agreed actions may include changing protection rules, working with the connectivity provider or escalating to the application administrator.
Aim and limitations
The outcome depends on the event and available controls. DDoS protection or application redesign requires a separately agreed scope.
Suspicious account activity in financial systems
Situation and assessment
Suspicious activity by an account with access to financial systems requires identity, session and related-event checks. An alert alone does not establish that data has leaked.
Team actions
SOC can restrict access within its permissions, examine available evidence and coordinate response. NOC supports assessment of the effect on the availability of in-scope services.
Aim and limitations
Operational records describe actions taken and limitations of the findings. Reporting duties and compliance with DORA or Poland’s National Cybersecurity System Act require a separate assessment; this scenario does not prove an absence of leakage or downtime.
Suspected ransomware in a public authority
Situation and assessment
Staff report inaccessible files while monitoring records widespread changes on a network share. SOC checks for signs of encryption and the extent of the incident; NOC identifies which public services are unavailable.
Team actions
Within its permissions, the team isolates affected assets, preserves available evidence and protects the backup environment. It agrees priorities for serving residents and a safe service recovery sequence with the authority.
Aim and limitations
The aim is to contain the attack and restore operations in a controlled way. Recovery time depends on incident scope, usable backups and addressing the cause of the compromise.
Further reading: CISA — #StopRansomware Guide
Unauthorised email forwarding in Microsoft 365
Situation and assessment
A mailbox rule forwards messages to an unfamiliar address. SOC analyses available sign-in and audit logs, checks whether the user authorised the change and investigates other signs of account compromise.
Team actions
An authorised team restricts access, revokes sessions and removes unauthorised rules. It resets the password in line with the identity setup and checks MFA methods, application consent and related activity.
Aim and limitations
The aim is to regain control of the account and assess possible information exposure. Removing a rule cannot recall forwarded messages; findings depend on available logs and their retention period.
Further reading: Microsoft — Respond to a compromised cloud email account
The backup succeeded, but the application will not start
Situation and assessment
During a planned test, a server is restored but the application does not work. NOC checks dependencies: the database, identity services, network and configuration. A successful backup job does not confirm recovery of the complete service.
Team actions
The team runs the agreed test in an isolated environment, documents missing dependencies and checks functionality with the application owner. It measures recovery time and the freshness of the restored data.
Aim and limitations
Results inform recovery procedure improvements and assessment of the agreed targets. The test covers a specified application and set of conditions; success does not guarantee the same outcome during a real incident.
Further reading: NIST SP 800-184 — Guide for Cybersecurity Event Recovery
These scenarios are educational. They illustrate possible sequences of events; they are not documented client engagements or promises of response time or service outcomes.
Questions and answers
Frequently asked questions about a 24/7 SOC and the VigilHorizon approach
How does your 24/7 SOC work?
A 24/7 SOC provides continuous event analysis and incident response as well as monitoring. We monitor infrastructure, logs, users and the network, then correlate the data using SIEM/XDR to detect real threats. The key difference is that we do more than see alerts: we analyse them and respond in real time.
Why is IT security monitoring not enough?
Monitoring generates alerts but does not provide analysis or response. Without a SOC:
• alerts remain unverified
• incidents develop unnoticed
• detection time increases significantly
Monitoring without response does not provide security.
Does NIS2 require a 24/7 SOC?
NIS2 requires appropriate and proportionate risk management measures, including incident handling. A 24/7 SOC can support these tasks, but monitoring and response should be organised according to risk and applicable requirements. Buying a plan does not confirm full organisational compliance.
Is SIEM without a SOC enough?
SIEM automatically correlates and analyses security data. Depending on the product, configuration and integration with SOAR or other tools, it can also trigger approved actions. Incident handling requires a process owner, business context, permissions, escalation rules and oversight of automation.
How quickly can you detect an incident?
Detection time (MTTD) depends on event context, but in the 24/7 SOC model, alerts are analysed in real time. The key principle is that detection time determines incident scale. The sooner an incident is detected, the smaller its impact.
What makes VigilHorizon different?
We provide operational capability rather than tools.
We combine:
• IT security monitoring
• event correlation (SIEM/XDR)
• incident management
• response playbooks
This enables us to detect an incident and stop it.
What happens when an incident occurs overnight?
If nobody owns out-of-hours alerts, response may be delayed. In the SOC 24/7 model:
• the alert is verified according to its priority and the agreed SLA
• a confirmed incident receives an owner and an escalation path
• an authorised response is carried out according to the playbook
This is why continuity of SOC operations is essential.
Contact
Unsure whether you will detect an incident in time?
Check whether your organisation’s alerts have a designated owner outside office hours too. Let’s discuss data sources, analysis, escalation and response permissions. This will help us agree which monitoring, SOC or NOC capabilities to include in our work together.
or